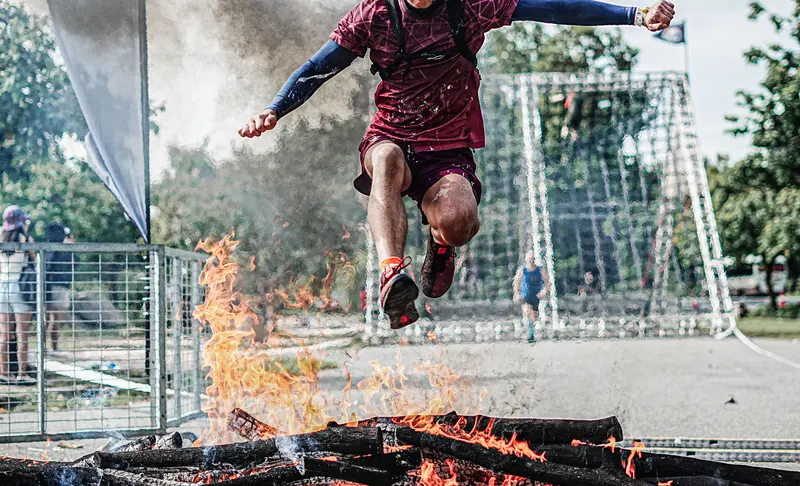
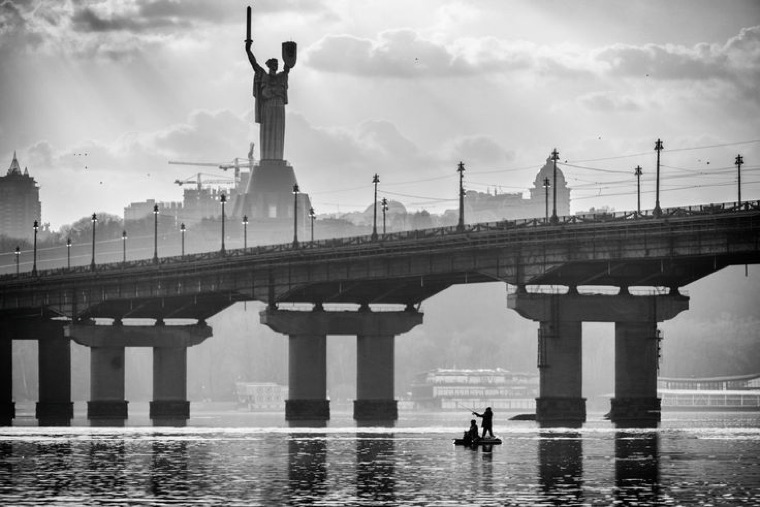
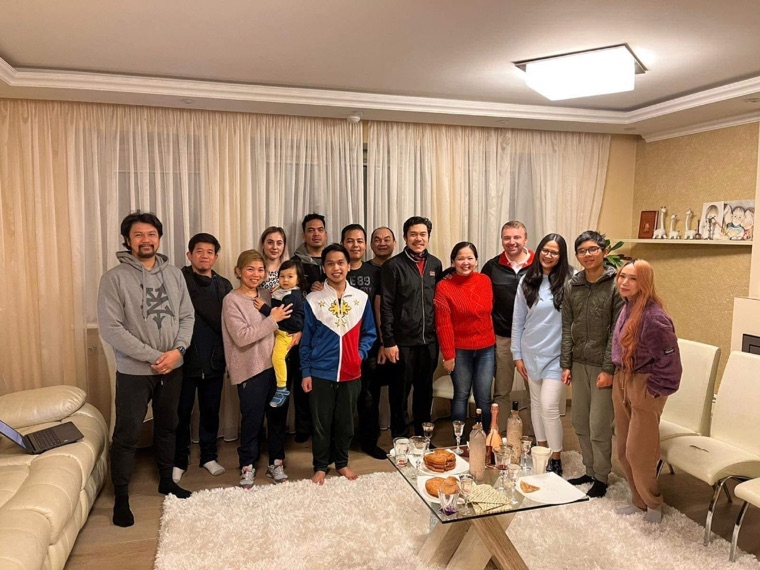
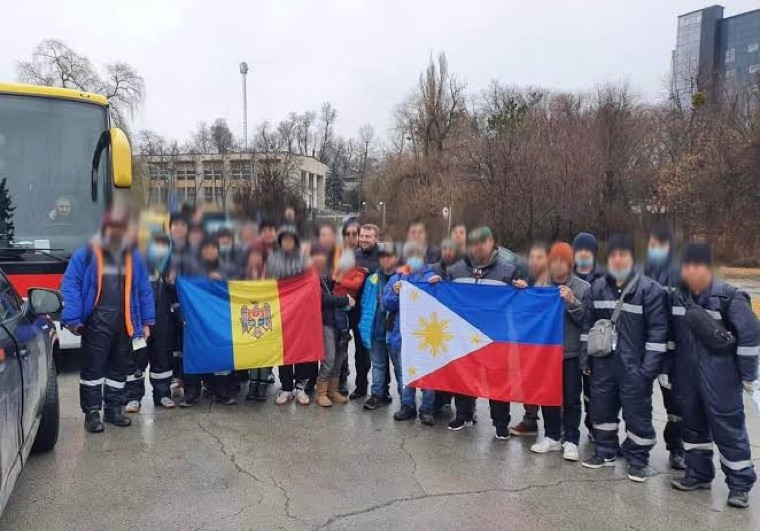
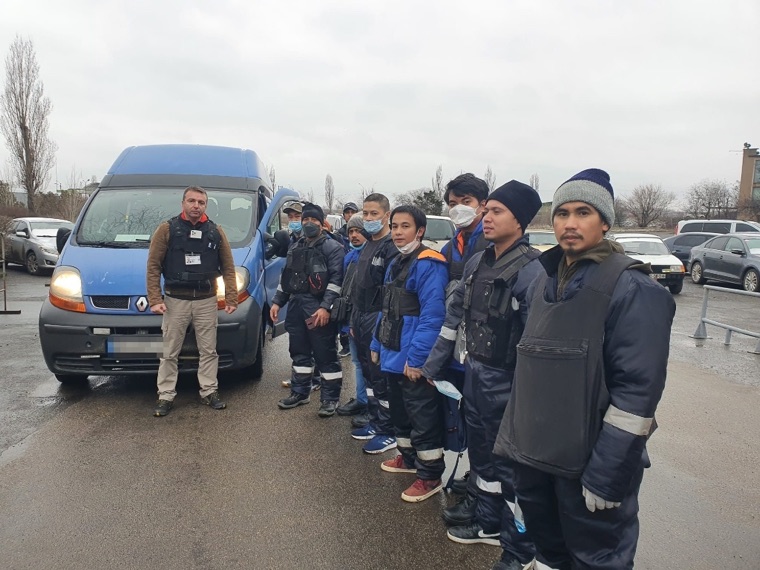
I grew up worldschooling across 30+ countries without a fixed classroom. Learning on the road meant seeing the world up close, from sharing stories in yurt camps to evacuating Ukraine in 2022 and helping stranded travelers in Bucharest navigate broken transit and financial corridors. Seeing how quickly critical systems can fail ordinary people is why I care so deeply about resilient engineering today.
Because I never had a traditional roadmap, I became an autodidact by necessity. I taught myself software engineering, cybersecurity, and machine learning from scratch using open documentation, YouTube, and Wikipedia, relying on my background as a tutor to translate complex theory into practical models.
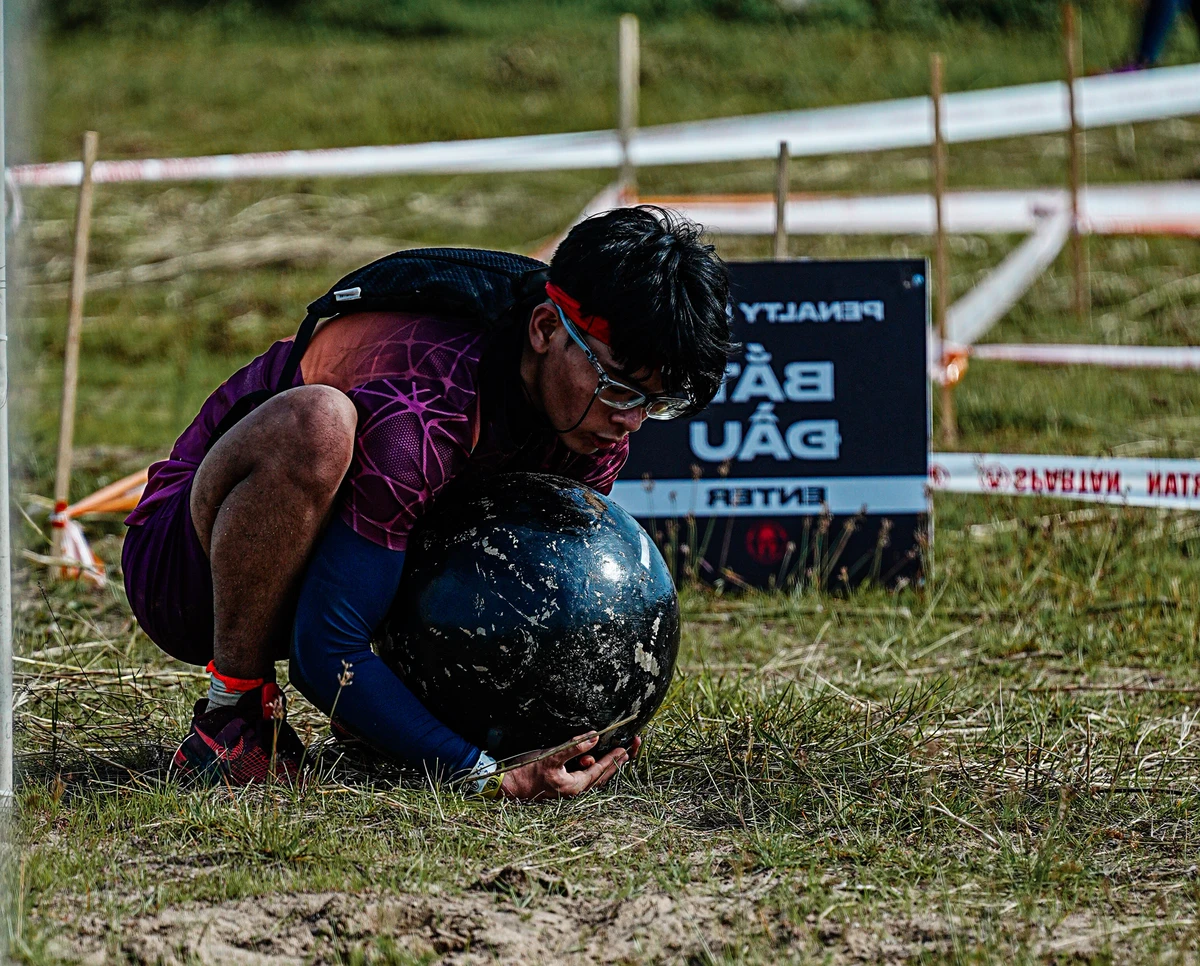
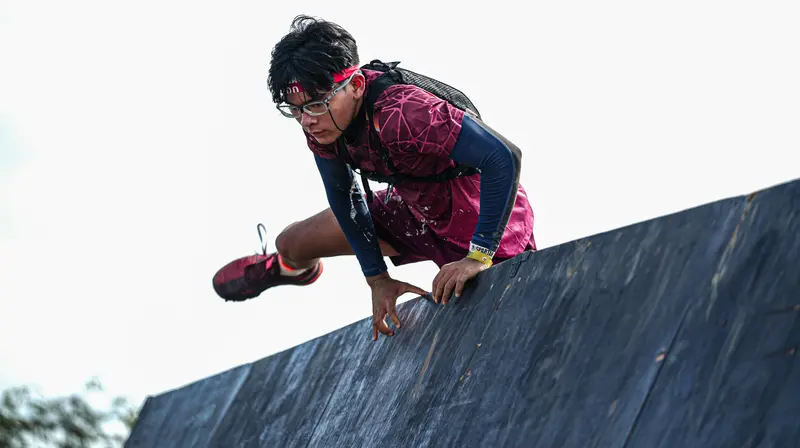
On the mats in Brazilian Jiu-Jitsu, out on marathon runs, and in the terminal, I live by the same rule: focus on the daily system rather than the outcome. Whether I am building Project Aghoy to protect families from scam networks or engineering internal AI and security tools, my goal is simple. I build reliable systems so people can spend less time worrying about infrastructure failing them and more time living actual human moments.
00
An interactive dithered globe choreographing the journey from worldschooling to Ukraine 2022, Bucharest safehouse staging, and Project Aghoy.
Pre-colonial Tagalog script meaning straight, upright, or uncorrupted.
Programmatic codification of ethics — constructing immutable guardrails where ambiguity creates systemic vulnerability.
SECTOR DOCTRINEGOV // INTEGRITY
02
⚙ CONTROL SPEC: STRICTAUDIT LVL 4
Governance
Creating fair rules where there are none. Technical governance is not bureaucratic friction; it is the programmatic codification of ethics and risk controls.
Production systems architecture, machine learning ranking infrastructure, and high-stakes operational security deployments.
02.1 // OPTICAL ARCHIVE
MZ-01 OPTICAL WORK ARCHIVE // FIVE RECORDSSILENT EVIDENCE PLAYBACK // NO AUDIO
3.1 Lab Infrastructure
Interactive defense systems, systems engineering, and vulnerability research.
[ SECTION 03 / 05 · PROJECTS ]
[SEARCH:]/
[ 01 // DIRECTORY ]6 AVAILABLE
01PROJECT_AGHOY
OPEN SOURCE
DEFENSIVE CYBER · TESSERACT.JS OCR
Anti-phishing SMS screenshot OCR and threat intelligence utility.
02PROJECT_VINLAND
OPEN SOURCE
PRODUCTIVITY · D3.JS GRAPH · CLI
Local-first browser workspace with personal wiki graph and command HUD.
03HIVEMIND
OPEN SOURCE
EDGE INFRASTRUCTURE · CLOUDFLARE WORKERS
Distributed edge network coordination with HMAC-SHA256 request signing.
04ARP_POISONING_MITM
RESEARCH
NETWORK SECURITY · SCAPY · DOCKER
Layer-2 packet injection, ARP cache poisoning, and PCAP forensics lab.
05XZ_BACKDOOR_ANALYSIS
RESEARCH
SUPPLY CHAIN · CVE-2024-3094 · GDB
Reverse engineering audit of GNU IFUNC symbol hijacking in liblzma.
06WANNACRY_IR_DASHBOARD
RESEARCH
INCIDENT RESPONSE · MS17-010 SMB
Incident Command simulation of EternalBlue exploits and killswitch sinkhole.
PROJECT_AGHOY
OPEN SOURCE
DEFENSIVE CYBER // CITIZEN THREAT INTEL
MOON DEF-NET // CRT-2084
MOON OS // 60Hz
CONTRAST
BRIGHT
TERMINAL // MOD-2084
PWR:
project-aghoy/package.json
Interactive security dashboard and gamified post-mortem analysis utility to recognize and report scams. Client-side OCR parses SMS screenshots without leaking data.
RUNTIME ARCHITECTUREReact 19 / TypeScript / WASM
SECURITY FOCUSClient-Side OCR Phishing Detection
ISOLATION ENVIRONMENTBrowser Sandbox (Zero Data Leakage)
CRYPTOGRAPHIC HASHSHA256: 7f8a39c1
React 19TypeScriptTesseract.js OCRRechartsWeb Crypto API
4.1 Credentials
Verification of specialized expertise and industry certifications.
[ SECTION 04 / 05 · REGISTRY ]
Fellow of Management Systems AuditingMASTERMIND // AI & PRIVACY
[FELLOW]
ISO/IEC 42001:2023 Lead AuditorMASTERMIND // AI GOVERNANCE
[AIMS]
ISO/IEC 27001:2022 Lead AuditorMASTERMIND // ISMS SECURITY
[ISMS]
ISO/IEC 27701:2025 Lead AuditorMASTERMIND // PRIVACY INFO
[PIMS]
OCI Foundations & AI AssociateORACLE // CLOUD SYSTEMS
[OCI-AI]
ISC2 Certified in Cybersecurity (CC)(ISC)² // CORE CYBERSECURITY
[CC]
IBM & ISC2 Cybersecurity SpecialistIBM & (ISC)² // SECURITY OPS
[SOC-OPS]
CS50's CybersecurityHARVARDX // ACADEMIC
[CS50]
International GED High School Equivalency DiplomaGED TESTING SERVICE // HIGH ACHIEVER
[HONORS]
[ ATTESTATION TELEMETRY CONSOLE ]
Fellow of Management Systems Auditing (FMSA)
ISSUER: MASTERMIND // AUDIT FELLOWSHIP · 2026
[FELLOW]
Audit Mandate & Scope
Senior fellowship in Management Systems Auditing. Authorizes dual-standard audit sign-offs across ISO/IEC 42001 (AI Management Systems) and ISO/IEC 27701 (Privacy Information Management).
Enforced ISO Control Clauses
DUAL AUDIT AUTHORIZATION[ENFORCED]
Authorized audit sign-off authority across ISO 42001 (AIMS) and ISO 27701 (PIMS).
EXECUTIVE GOVERNANCE REVIEW[VERIFIED]
Senior risk assessment, threat mitigation planning, and executive audit sign-off.
Full inventory: every entry has shipped in a project, engagement, or audit on this site.
No proficiency theater; ask me about any of them.
[ SECTION 05 / 05 · TOOLCHAIN ]
Core Stack // 12 of 44
Python
C++
JavaScript
SQL
Bash
HTML / CSS
Cloudflare Workers
Cloudflare D1
Cloudflare R2
REST API design
Rule-based NLP
ISO/IEC 27001
ISO/IEC 42001
ISO/IEC 27701
Wireshark
Scapy
tcpdump
OSINT
OpSec / VPN hardening
Incident response
Cloudflare Pages
Wrangler
Docker
OCI
VM lab environments
Three.js
D3.js
Canvas API
Tailwind CSS
GSAP
Browser extensions
LangChain / LangGraph
LLM API integration
Agent orchestration
Model routing / eval
Open-weight models
Git
SQLite
Linux Commands
CSP / security headers
WebGL2
Cloudflare Pages
ipwho.is API
Google Fonts API
TOOLCHAIN_COUNT: 44 ENTRIES // FILTER: ALL
SELECT A TOOL TO INSPECT
Dialog
PRIVACY // BROWSER BROADCAST
CLIENT-SIDE // LOCAL CACHE
What this page can see
Every request carries some data. This panel is a transparent readout of what your browser exposes to a website. The geo lookup runs only when you open this disclosure, and nothing here is sent to a Monozen analytics endpoint.
> SESSION // VISITOR TELEMETRY DISCLOSURE
NET_ID-
GEO-
COORD-
ISP-
UA-
SCREEN-
TZ-
LANG-
CORES-
MEM-
DNT-
COOKIES-
> SCAN PENDING…
Every website you visit receives this data silently. The difference here is that you can see it.
The geo lookup is sent to ipwho.is only when you open this panel. The result is cached in your browser's local storage to avoid repeat lookups.
No first-party analytics, advertising, or cross-site tracking cookies are set by this site.
This disclosure is static. There is no chat, no query input, and no server-side profile.
Protecting livelihoods against more than social engineering. In an increasingly connected world, cybersecurity is the baseline for human throughput and infrastructure survival. My work centers on network traffic forensics, zero-trust perimeter defense, and operational security across untrusted environments.
Engineering Philosophy & Stance
Zero-Trust Execution - Perimeter defense is dead. Every service connection, endpoint, and packet is untrusted until cryptographically verified.
Global OpSec & Network Hardening - Real-world operational security protecting communications and remote access across 30+ untrusted country networks and 250+ transit environments.
Traffic Forensics & Packet Analysis - Low-level network inspection using packet analyzers and custom scriptable capture tools to isolate threat vectors before escalation.
Creating fair, deterministic rules where there are none. Technical governance is not bureaucratic friction; it is the programmatic codification of ethics, privacy, and compliance directly into software runtime so technology serves human agency.
Engineering Philosophy & Stance
Programmatic Guardrails - Enforcing safety policies and compliance controls directly at the code execution layer rather than relying on manual policy documents.
AI Systems Management (ISO 42001) - Implementing international standards for responsible AI deployment, risk mitigation, and algorithmic accountability.
Privacy & Data Lineage (ISO 27701) - Architecting secure storage and edge ledgers that uphold user privacy management by default.
Engineering resilient internal AI infrastructure that bridges security policy with ground-level machine learning execution. Moving past chatbot wrappers to build production-grade agentic workflows, model routing, and deterministic evaluation harnesses.
Engineering Philosophy & Stance
Deterministic Machine Safety - Guarding non-deterministic neural network outputs with strict schema validation, structured output engines, and evaluation harnesses.
Multi-Agent Orchestration - Architecting stateful, multi-step agent workflows that execute complex tasks reliably without human bottlenecking.
Model Routing & Edge Integration - Balancing cost, speed, and privacy by routing requests across open-weight models and edge runtime workers.
Developing Machine Learning models and data processing pipeline solutions to enhance data analysis, search, and intelligent ranking workflows.
Status
Active Internship · Ongoing
Core Focus
ML Pipeline Development - Building and maintaining scalable data processing pipelines for model training and evaluation.
Model Research & Optimization - Testing and evaluating ML architectures for search relevance, embeddings, and ranking accuracy.
System Integration - Integrating ML service endpoints into production workflows.
Embedded directly into commercial operations to resolve architecture bottlenecks, replace legacy agency dependencies, and engineer cloud infrastructure, ingestion pipelines, and search indexing.
Status
Active Engagement · Ongoing Contract
Core Infrastructure & Scaling
Web Traffic & Search Rankings - Re-engineered legacy monolith architecture into statically pre-rendered Next.js on Cloudflare Edge, scaling organic reach to 100,000+ unique prospective client visits in <30 days and securing Rank #1 on Google for primary commercial practice terms.
10× Latency Reduction & Performance - Migrated vulnerable PHP/MySQL infrastructure to a serverless edge architecture, reducing page load times from 4.8s to <350ms (10× faster) with a verified 100/100 Core Web Vitals score across 49+ routes.
Systems Availability & Compliance
Resilient Data Ingestion & Recovery - Diagnosed an upstream API schema defect silently dropping 100% of inbound client inquiries; engineered an automated serverless intake pipeline backed by a 30-day durable Cloudflare KV fallback queue that guaranteed zero data loss.
Automated CI/CD Checks & Security - Engineered automated pre-deployment checks in TypeScript, programmatically halting production releases that violate regulatory advertising rules, contain hardcoded credentials, or expose PII.
Data Architecture & Cost Efficiency
AI Knowledge Graph Architecture - Engineered structured semantic markup and multi-tier Schema.org Knowledge Graphs, enabling direct entity ingestion, indexing, and citation across AI search engines (ChatGPT, Claude, Perplexity).
Cost Elimination & Brand Security - Eliminated $50,000+ in outsourced agency fees and $60,000/year in retainers via in-house cloud infrastructure; secured 12 defensive domain variations under Cloudflare to protect brand presence and prevent squatting.
Independent educator managing curriculum design, student performance tracking, and high-volume remote instruction for international learners.
Scaled instruction - Delivered live instruction to 100+ students across 10+ countries, adapting pedagogy across CEFR A1–C2.
Performance analytics - Engineered a custom student-tracking framework to monitor KPIs, isolate learning deficiencies, and adjust trajectories in real time.
Structured feedback - Produced post-session analytical reports for 100% of sessions with metric-driven visibility.
High-volume logistics - Managed a peak 52-hour weekly caseload across time zones with 100% attendance compliance.
Outcomes - Guided students to Distinction/140+ KET, Band 7.0–8.0 IELTS, and successful US Student Visa approvals.
Sole operations & technical lead for a globally traveling executive across multiple countries.
Sole IT administrator - End-to-end IT for a mobile executive office; uninterrupted connectivity across 30+ countries and 250+ transit environments.
Network & OpSec - Configured and secured VPN and remote access across 100+ untrusted public networks, protecting comms across 30+ jurisdictions.
Global connectivity - Managed eSIM/SIM provisioning and cross-border cellular configs with 100% uptime for critical comms.
OSINT - Conducted OSINT audits on 500+ service providers and hosts, identifying risk indicators to prevent fraud or safety incidents.
Provided English instruction and cultural exchange across Ukraine, Myanmar, Nepal, and Vietnam - focusing on communities facing economic instability or geopolitical transition.
Geopolitical adaptability - Delivered support in high-tension environments preceding major political shifts, requiring rapid adaptation.
Cross-cultural integration - Bridged linguistic gaps and maintained educational continuity despite external uncertainties.
Resource management - Adapted teaching methods for resource-constrained settings with minimal infrastructure.
Free and open-source citizen security utility for mapping, analyzing, and warning communities about predatory scam networks in the Philippines. Born from personal experience when family members were targeted by SMS phishing rings - turning private defense into a public-facing threat intelligence tool.
Engineering & Security Architecture
Tesseract.js 7.0 OCR engine - Instant optical character recognition extracted from SMS screenshots directly in the browser sandbox.
Verdict matrix engine - Algorithmic evaluation scoring risk (`SAFE`, `SUSPICIOUS`, `HIGH_RISK`) across task scams, investment schemes, and impersonation vector patterns.
Web Crypto & Recharts HUD - Cryptographic hashing of report signals coupled with interactive threat breakdown charts.
Community report verification - Crowdsourced dispute and verification workflow to filter noise and preserve signal integrity.
Empirical Benchmarks & System Tradeoffs
Client-Side Execution Tradeoff - Swapped server-side OCR endpoints for WebAssembly-compiled Tesseract.js, eliminating server processing costs while achieving 100% offline user privacy.
Client OCR Latency Benchmark - Average 1.2s local screenshot parsing time; 0ms network latency; 0 byte data leakage to external APIs.
Client-side browser extension workspace replacing New Tab with a keyboard-first command interface. Named after Vinland Saga ("A place beyond all fighting - peace on the other side of pain"), built to reclaim human attention from algorithmic distraction loops through local-first software engineering.
Internal Tooling Architecture
Manifest V3 & Service Worker - Isolated background boot pipeline managing cross-tab Pomodoro state, bookmarks, and `declarativeNetRequest` rule filters.
Tactical overlay and edge-accelerated intelligence network engineered to coordinate complex multi-agent maneuver loops under intense real-time demand without server exhaustion.
Performance & Cryptographic Architecture
97% TTFB reduction (<45ms) - Custom `withCache` middleware utilizing Cloudflare Cache API (`caches.default`) reducing edge response time from 1500ms to <45ms.
HMAC-SHA256 JWT security layer - Web Crypto API authorization enforcing non-repudiation and role-based access control (RBAC) on all tactical requests.
Antzzzbase strategic intelligence engine - 500-entry rolling snapshot window with 90-day retention tracking enemy habit trends and troop compositions.
Hands-on network-layer security audit evaluating Layer-2 vulnerabilities in a multi-host ARM64 VM and Docker lab subnet simulating corporate network infrastructure.
Security Audit Demonstrations
Scapy packet forging - Custom Python scripts crafting raw ARP cache corruption packets and forged TCP frames.
MITM TCP stream interception - Live interception, payload logging, and modification of active TCP sessions between victim nodes.
Root Cause - Fundamental lack of authentication in ARP (RFC 826) protocol allowing stateless cache overwrite across local Ethernet segments.
Attack Vector - Unsolicited gratuitous ARP reply injection mapping gateway IP (`192.168.1.1`) to attacker MAC address (`02:42:ac:11:00:02`).
Remediation & Countermeasures - Enforced Dynamic ARP Inspection (DAI) on managed switches and static ARP table bindings (`arp -s`).
WiresharkScapyDockerPythontcpdump
Independent technical analysis of the CVE-2024-3094 XZ Utils supply-chain backdoor - dissecting the multi-year social engineering campaign and stealth binary injection into Linux system compression libraries.
Vulnerability Research Findings
IFUNC symbol redirection disassembly - Traced GNU indirect function (IFUNC) hooks used to hijack SSHD authentication functions (`RSA_public_decrypt`).
Liblzma injection vector - Dissected how malicious build stages injected pre-built object files during binary packaging.
Threat governance model - Mapped adversary tactics against OWASP and supply-chain governance frameworks.
Incident Post-Mortem & Forensic Audit
Root Cause - Multi-year social engineering campaign acquiring co-maintainership of `xz-utils`, inserting obfuscated M4 macro build hooks into release tarballs.
Attack Vector - GNU `IFUNC` function redirection hijacking `RSA_public_decrypt` in `liblzma.so` during `sshd` startup, enabling unauthorized RCE via forged RSA signatures.
Remediation & Governance Impact - Immediate revocation of compromised tarball signatures, widespread deployment of audit tools, and revision of open-source maintainer governance models.
Browser-based Incident Command Center simulating forensic post-mortem analysis and incident response workflows for the 2017 WannaCry ransomware attack.
Forensic & UI Architecture
EternalBlue SMBv1 exploit analysis - Dissected the MS17-010 vulnerability and worm propagation mechanics across enterprise networks.
Kill-switch domain verification - Visualized the hardcoded kill-switch domain lookup (`iuqerfsodp9ifjaposdfjhgosurijfaewrwergweba.com`) and containment timeline.
Interactive Command HUD - Built an 8-bit/cyberpunk CRT interface with simulated AI Incident Commander response logs.
Incident Post-Mortem & Forensic Audit
Root Cause - Unpatched Windows SMBv1 buffer overflow vulnerability (MS17-010 / EternalBlue) combined with automated NSA DoublePulsar backdoor injection.
Attack Vector - Rapid network propagation via TCP ports 445/139 without user interaction, executing AES-128 payload encryption across target filesystems.
Remediation & Containment - Emergency deployment of Microsoft MS17-010 security patch, blocking port 445 at edge firewalls, and sinkholing hardcoded kill-switch domain.
Highest management systems auditing fellowship covering both AI management (ISO/IEC 42001:2023) and privacy information management (ISO/IEC 27701:2025).
ISO/IEC 42001ISO/IEC 27701AI GovernancePrivacy
Lead Auditor certification for Information Security Management Systems (ISMS).
ISMSAudit PlanningRisk Management
Lead Auditor certification for AI Management Systems - the first international standard for AI management.
AI GovernanceAI Risk Management
Lead Auditor certification for Privacy Information Management Systems (PIMS) - the privacy extension to ISO/IEC 27001.
ISO/IEC 27701PrivacyAudit Planning
Two Oracle Cloud Infrastructure 2025 certifications covering core cloud architecture (IaaS, PaaS, SaaS) and the foundational frameworks of AI, ML, and generative AI on OCI.
Rigorous program covering fundamentals of information security, threat modeling, and risk management. Engaging with the global CS50 community directly inspired pursuing Python.
Earned a U.S. high school equivalency diploma with a score of 694, placing in the top 1% of test-takers globally. Achieved through one month of self-directed study across all four subjects.
This is a static personal portfolio. It does not run first-party analytics, advertising, or a server-side visitor profile. The optional telemetry disclosure is client-side and runs only when you open it.
Data the browser exposes
Request metadata - IP address and approximate geolocation from ipwho.is, requested only when you open the PRIVACY disclosure. The result is cached in localStorage (`mz-geo-cache`) to avoid repeating the request.
Browser fingerprint - User agent, screen size and color depth, timezone, language, CPU cores, device memory, Do Not Track, and cookie-enabled status. Used solely for the disclosure and not sent to a Monozen analytics endpoint.
No hidden collection - This site does not add GPU renderer, canvas hash, battery, referrer, or behavioral analytics collection of its own.
Storage & Control
No tracking cookies - No first-party analytics or advertising cookies are set by this site's code. Cloudflare, CDN, and font providers may process requests and keep standard logs under their own policies.
Local browser storage - Theme (`mz-theme`), boot state (`mz-booted`), telemetry cache (`mz-geo-cache`), opt-out (`grc-opt-out`), and front-door state (`mz-entry-seen`). Clear site data to remove them.
Opt-out - If `grc-opt-out` is set, the disclosure is redacted before any lookup and no ipwho.is request runs.
No server profile - The disclosure data is not stored on a Monozen server, sold, or used for advertising.
Third parties
ipwho.is - IP geolocation, only when the disclosure is opened. Their privacy policy applies.
Google Fonts, esm.sh, cdnjs, Cloudflare - Fonts, CDN libraries, and hosting. Each processes requests under its own privacy policy.
Contact
rhyonfs@gmail.com - Data subject requests handled within 30 days per GDPR Art. 12.
This website is a personal portfolio presented for professional evaluation. Access constitutes acceptance of the following terms.
Use of Content
Personal portfolio context - All content (text, code samples, certification data) is presented as a representation of professional qualifications. Reproduction for commercial purposes is prohibited.
No warranties - The site is provided "as is" with no guarantees of availability, accuracy, or completeness. The author is not responsible for third-party content linked from this site.
Interactive Features
Privacy disclosure - The footer PRIVACY control opens a static readout of the data your browser exposes. There is no chat input, no query history, and no server-side profile.
No user accounts - There is no login, no comment system, and no persistent user session beyond the theme preference in localStorage.
Liability
The author shall not be held liable for any damages arising from use of this site or reliance on its content. All technical demonstrations are illustrative and should not be deployed without independent review.
This site operates on a zero-cookie policy for tracking purposes. The only data persisted in your browser is local site state: theme, boot state, telemetry cache, opt-out preference, and front-door entry state.
localStorage Items
mz-theme - Stores your selected theme (moon). No expiration. Cleared via localStorage.removeItem('mz-theme').
mz-booted - Marks that you've seen the boot sequence once, so returning visits skip it. No expiration. Cleared via localStorage.removeItem('mz-booted').
grc-opt-out - Stores telemetry opt-out preference. Read before any data collection begins.
mz-geo-cache - Caches the last ipwho.is response locally so the disclosure does not repeat the lookup. Cleared with the rest of the site data.
mz-entry-seen - Persists the front-door entry state so return visits and new tabs skip the intro. Cleared with site data.
Third-Party Requests
assets/tailwind.css - Utility CSS framework (local build, no external requests).
fonts.googleapis.com / fonts.gstatic.com - Font loading. Google's privacy policy applies.
esm.sh - CDN for Three.js. No cookies.
ipwho.is - IP geolocation, requested only when the privacy disclosure is opened. Their rate limits and privacy policy apply.
Managing Preferences
Open PRIVACY in the footer to inspect what this page can see. If grc-opt-out is set, the lookup is redacted before it runs. No cookie consent banner is displayed because no tracking cookies are used.